AI governance · European mid-market
See where AI flows through your organisation.
SiyadAI turns AI usage signals — browser extension, proxy logs or declarations — into a governable inventory, risk decisions and usable evidence.
No prompts, no content, no business files
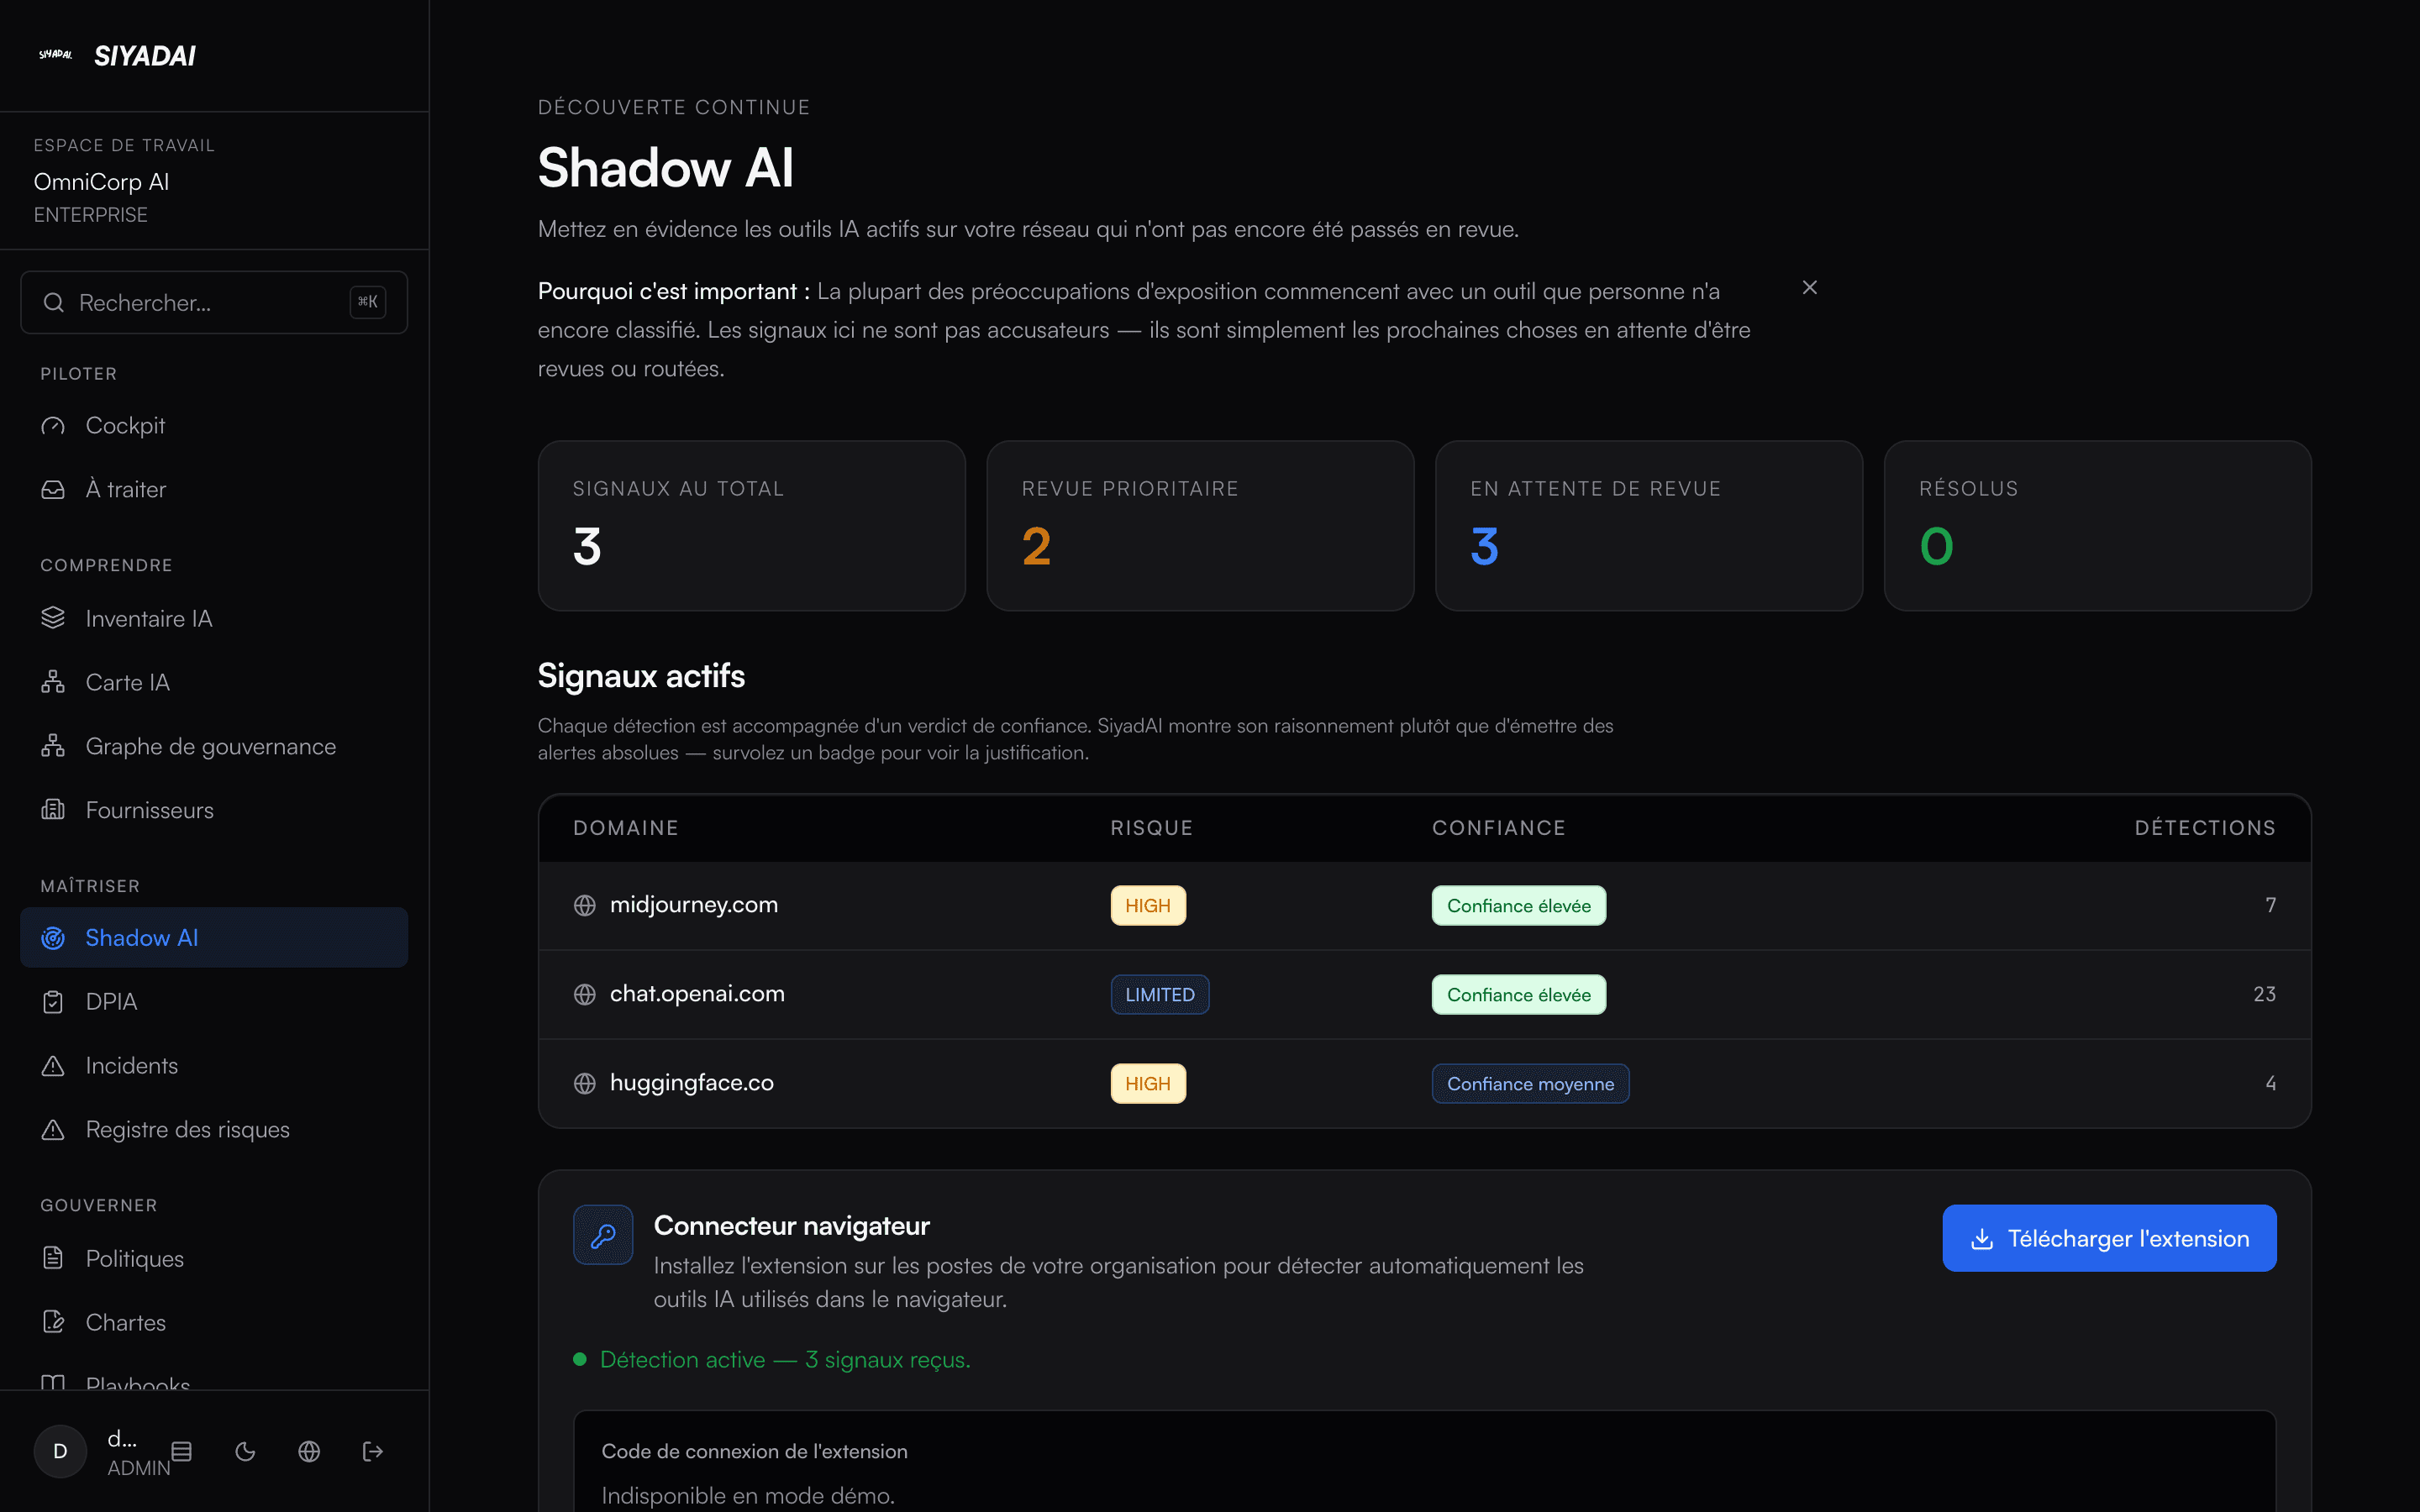
Start with the signals you already have.
Three ways to feed the register. None of them asks you to change your infrastructure.
Browser extension
Detects AI tools opened in the browser, by domain name. No prompt, no response, no content.
Chrome and Edge
Proxy logs
You export a CSV from your proxy or gateway. The file is parsed on your own machine; only per-domain counters are sent.
CSV import, local parsing
Declarations
Teams declare the tools they use, and the register receives them alongside everything else.
Unlimited reporters
SiyadAI does not connect to your proxy: you export, you import. No native connector is offered today.
Your infrastructure detects. SiyadAI governs.
A proxy produces a signal. An extension observes a usage. An employee declares a tool.
None of the three answers the questions an audit asks.
What a signal does not tell you
- Which tool, exactly?
- For what business purpose?
- Who is accountable for it?
- Which data is involved?
- What level of risk?
- What decision was taken?
- What action followed?
- What evidence remains?
SiyadAI turns the signal into governance.
From signal to evidence, without a gap.
Six stages. Each leaves a dated trace, and each exists in the product today.
- 1
Signal
Extension, proxy logs or declaration: a usage appears.
- 2
Inventory
The usage enters the AI system register, with its source and date.
- 3
Qualification
Role, purpose, data involved, classification under the EU AI Act.
- 4
Decision
Allow, restrict or refuse — with a named owner and a written reason.
- 5
Action
The decision becomes an assigned task, with a deadline and follow-up.
- 6
Evidence
A sealed, timestamped Evidence Pack, verifiable without a SiyadAI account.
A detected domain is not a risk yet.
Between a raw signal and a defensible decision there are six steps. Most tools stop at the first.
- Domain observed
- Tool identified
- Usage qualified
- Owner named
- Decision recorded
- Tracked over time
The rule that avoids false comfort
A recognised tool enters the register as “to qualify” — never as “compliant”. The EU AI Act classifies a system by its purpose, and that purpose is yours to know.
Domains the catalogue does not recognise
They are not counted as AI: a domain name alone cannot establish that. You see them with their volume and you decide — ignore, track as a usage to qualify, or flag them for review.
Govern how AI is used. Not what your teams write.
A proxy export contains user identifiers, IP addresses and full URLs. It is parsed on your own machine, line by line, and does not leave it.
What never leaves
- Prompts and responses
- File contents
- Full URLs, paths and parameters
- IP addresses
- User identifiers
What is sent
- The domain name recognised in the catalogue
- The number of requests
- The first and last dates observed
- The signal source
64 MB of logs parsed locally. 1.7 KB sent.
Measured on 500,000 lines and 12 distinct AI tools. What is sent depends on the number of recognised tools, not on the size of the file.
- EU hosting & processingApplication, API and database in the European Union
- Built for the EU AI ActRegister, classification, dated evidence
- Minimal signalDomain names — never your prompts
- Per-organisation isolationMFA, RBAC, full audit log
Do not audit your data leaks with a tool that leaks your data.
Plenty of organisations check their use of American AI… with tools that analyse their content outside Europe.
The common approach
Log and content analysis through servers outside the EU. Your AI traffic leaves Europe in order to be audited.
SiyadAI
A minimal-signal extension: domain names only, never your prompts or your content. Imported logs are parsed on your own machine — only per-domain counters are sent.
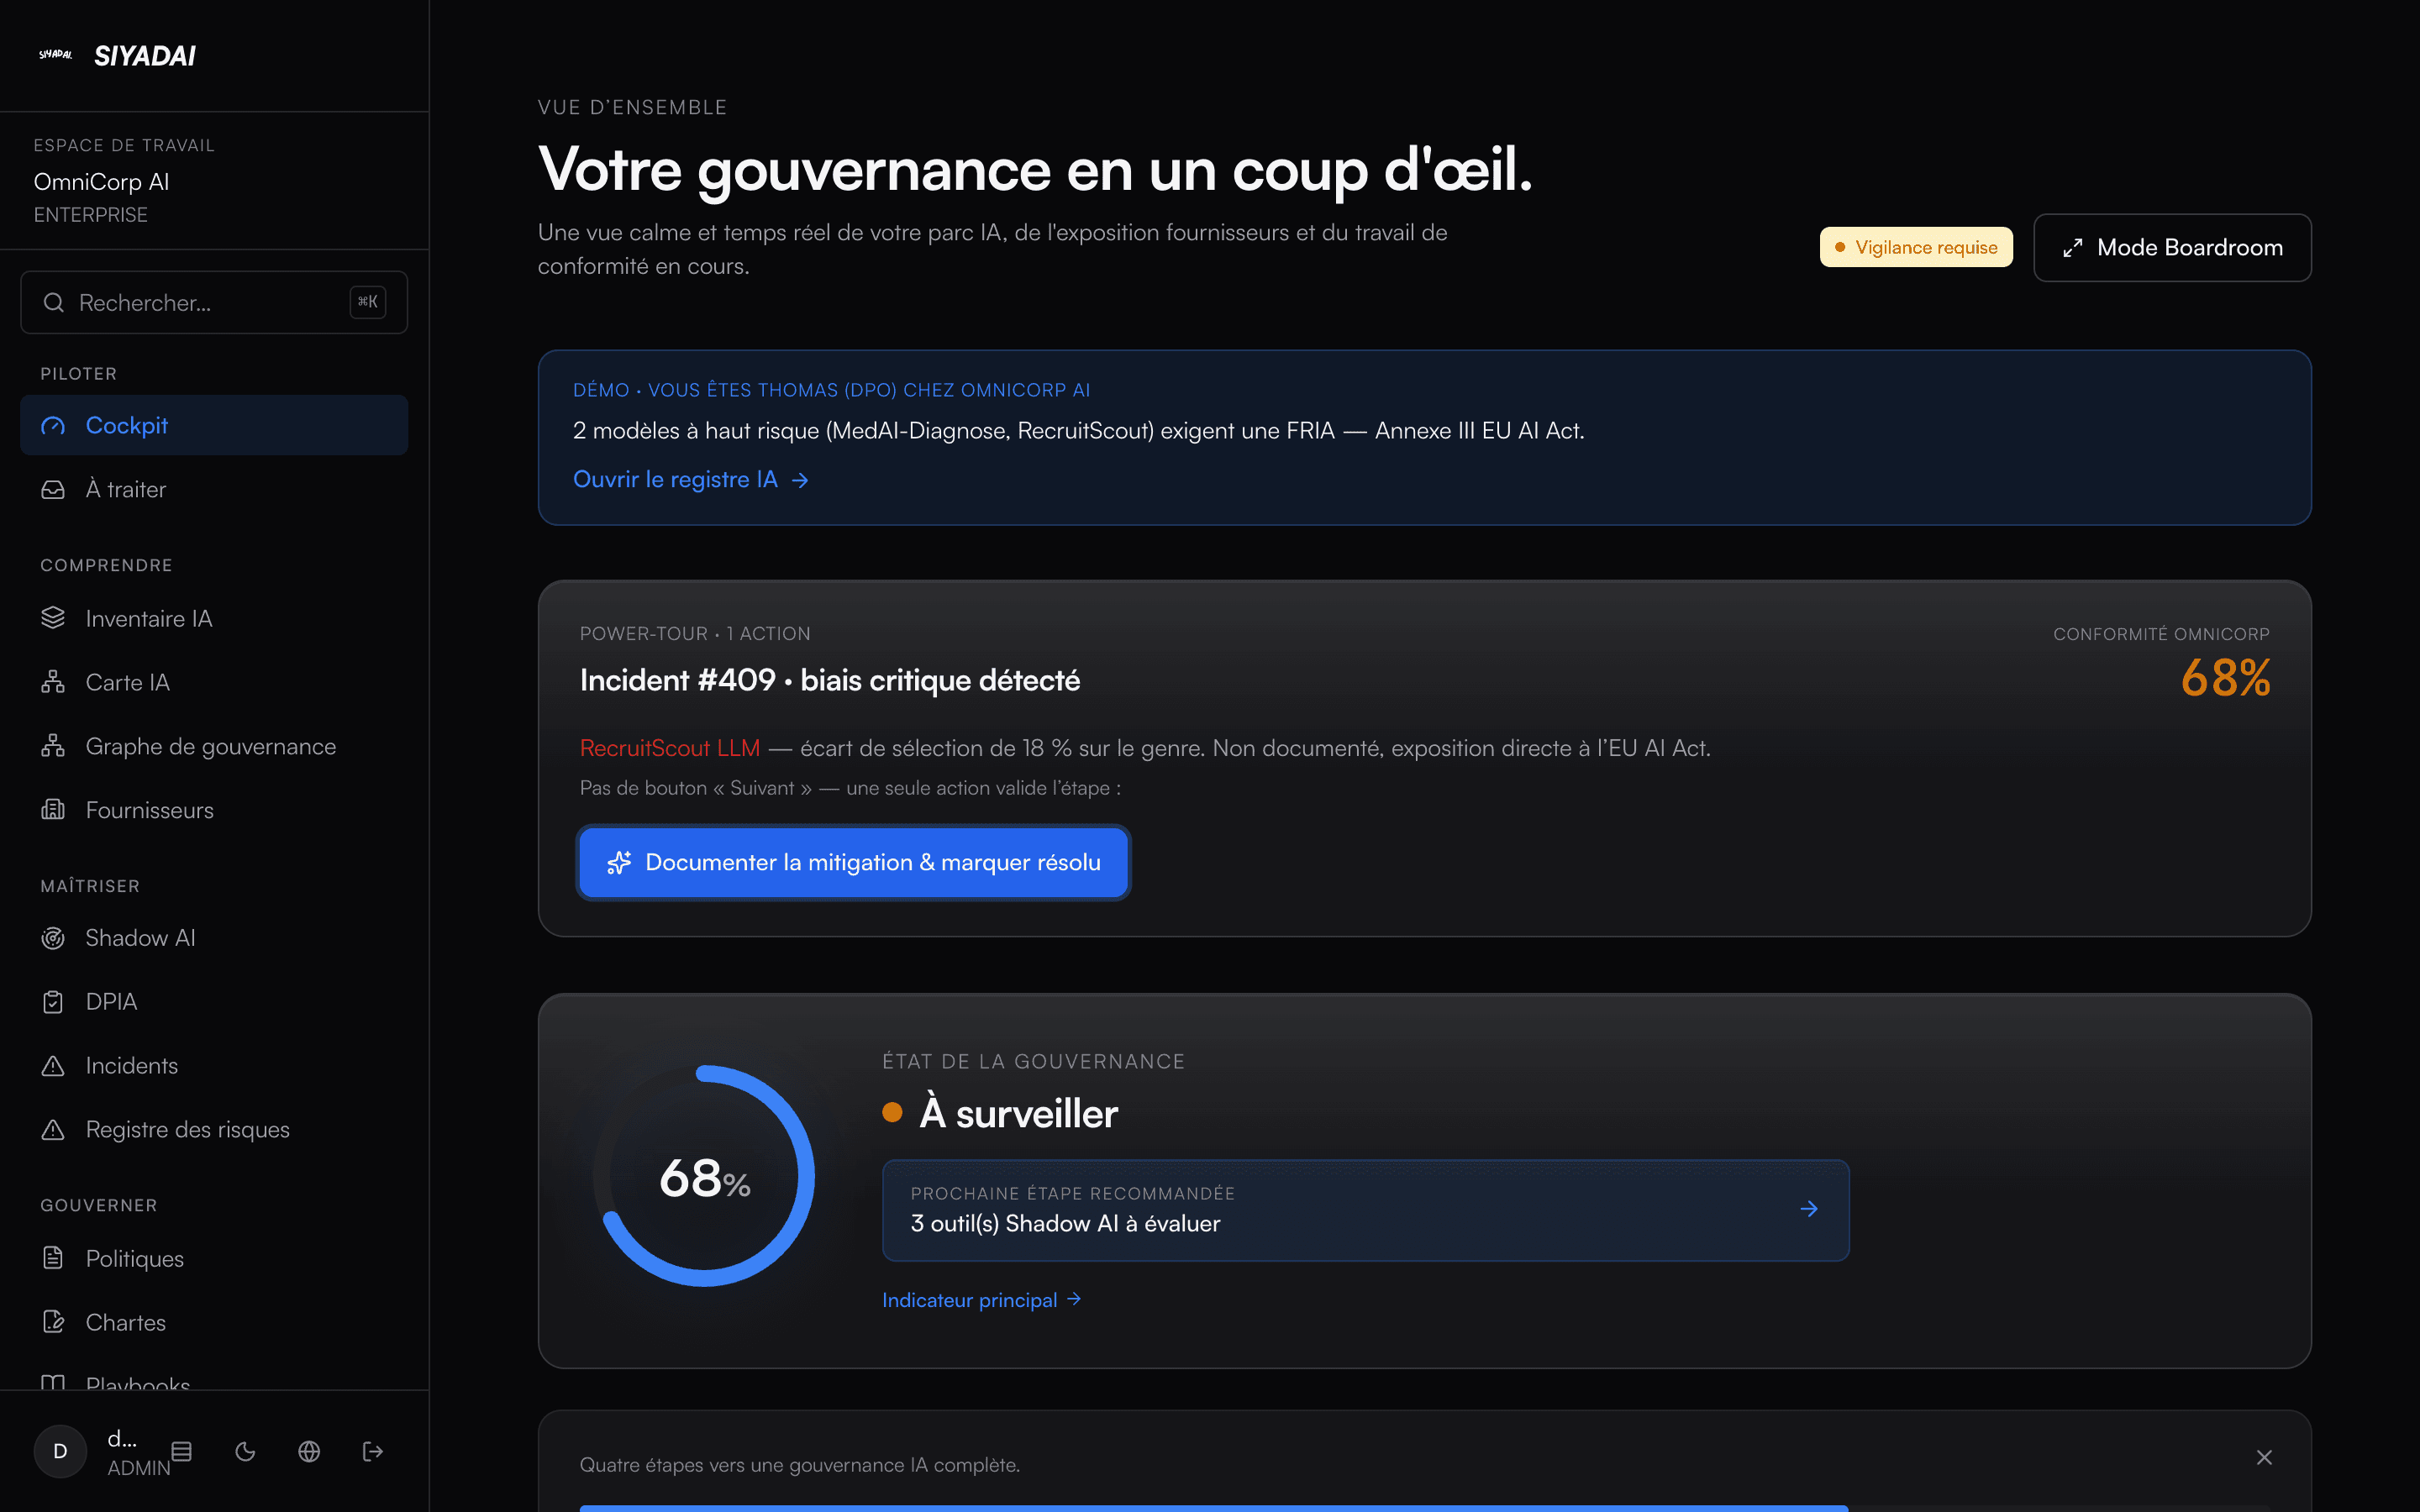
This is what you see, from day one.
Not a promise: the real interface, populated with a representative AI estate. Open the demo and walk through it yourself.
OmniCorp compliance
68%
Vigilance requiseMedAI-Diagnose v2.4
Aide au diagnostic médical
RecruitScout LLM
Tri et scoring de candidatures
OmniChat Support
Chatbot de support client
CodeHelper Copilot
Assistant de code interne
Every system classified, dated and justified — the artefact an auditor asks for.
Noms de domaine uniquement — jamais vos prompts ni vos contenus.
Incident #409
RecruitScout LLM — an 18% selection gap on gender.
The posture updates immediately — and the decision stays on record.
Built for organisations that intend to stay in control of their AI
Security
- Data hosted in the EU, encrypted, isolated per organisation.
- MFA, role-based access, full audit log.
Compliance
- Built for the GDPR and EU AI Act framework.
- Evidence Packs, signed briefs, verifiable exports.
Control
- You keep control of your data and your access.
- Nothing to install for the demo, no commitment.
Quel est votre score d’exposition au Shadow AI ?
Four questions. An immediate estimate of how many AI tools escape your governance.
Detection starts in the browser.
L’extension reconnaît les outils d’IA que vos équipes ouvrent — by domain name, never the content of your prompts . Installed in 60 seconds, it keeps your register current.
Examinée par Google · Chrome et Edge · Aucun compte requis
The cost of doing nothing.
Every month without visibility is a month of data slipping out and evidence going missing.
The market is full of AI registers.
No virtual governance officers.
AIGO writes your governance brief every week — deterministic, reproducible, sealed with SHA-256 — and delivers it to your DPO by email and as a board-ready PDF.
Brief de gouvernance — semaine 29
sha256 9f2c4e7a1b8d3f60c5a94e2b7d18f0a3c6e5b492d7a1c8f3e0b6d245a9c71e8f
· exemple
Chaque brief est vérifiable publiquement, sans compte — see how verification works.
Surveille
Parc IA, fournisseurs et détections Shadow AI, en continu.
Détecte
Risques hiérarchisés : AIPD manquantes, incidents, alertes réglementaires.
Documente
Brief hebdomadaire horodaté et scellé, journal d’audit complet.
Recommande
Plans d’action 30 et 90 jours, classés par impact.
Prépare l’audit
Synthèse AI Act / RGPD et Evidence Packs vérifiables.
Built for the European regulatory framework
EU AI Act
Aligned with the 2025–2027 deadlines
GDPR · UK GDPR
Registers, DPIAs, data subject rights
EU hosting
Data hosted and processed in the EU
EUR-Lex · monitoring
Texts tracked continuously
Built for regulated sectors: Finance & Insurance · Healthcare · IT Services & Consulting · Industry · Public sector
Enterprise-grade security
- Isolation par organisation (RLS)
- MFA TOTP
- RBAC · Admin / DPO / CISO
- Journal d’audit complet
- Sauvegardes chiffrées hors fournisseur
- Exports vérifiables (QR)
Complements your infrastructure, does not replace it
Your proxy detects, your SIEM collects, your register documents. SiyadAI connects the signals, the decisions and the evidence. Entra ID SSO and ITSM tickets are wired in; logs are exported from your own tools and imported here.
A plan for every level of maturity.
The price of one governance hire, the work of a team. The 14-day Shadow AI audit is free; the plans cover full governance.
Programme Fondateurs — 10 places · price locked for 24 months, founder-led onboarding, roadmap influence →Starter
Your Governance Officer, part-time
490 €/ month, excl. VAT
€5,880/year — or €4,900/year billed annually
- Discover every AI tool genuinely in use across your teams
- Know which ones carry risk, without being an expert on the subject
- Build the defensible AI register the EU AI Act expects
- Put a first picture in front of your board within a week
- Stop tracking AI usage in a spreadsheet
- AI register, 20 systems with automatic scoring
Business
Most chosenYour Governance Officer, full-time
990 €/ month, excl. VAT
€11,880/year — or €9,900/year billed annually
- Your AI Act compliance documents itself, continuously, without you thinking about it
- Produce signed, timestamped audit evidence on demand, in one click
- Risks prioritised and assigned automatically, without a committee
- Every AI decision traced, justified and defensible
- Answer a regulator or an enterprise buyer in hours, not weeks
- Unlimited systems and vendors
Enterprise
A governance team for the whole group
From €2,400/ month, excl. VAT
multi-entity · SSO · contractual SLA
- Steer AI compliance across all your entities from a consolidated view
- Measure the impact of a vendor change before it becomes an incident
- Apply your own governance rules, not a vendor’s
- Leave each entity its autonomy, give the group its visibility
- Pass group audits with a single, verifiable chain of evidence
- One AIGO per entity + group consolidation
Prices excl. VAT · hosting entirely in the EU · 2 months free on annual billing · 12-month or flexible commitment (+20%). Discovery: a 14-day Shadow AI audit, no card — Shadow AI scanning, 5 systems, unlimited reporting. When the audit ends the workspace becomes read-only: your data stays accessible and exportable. See full plan details →
See SiyadAI on your own estate.
See SiyadAI on your own estate.
- Audit d’exposition Shadow AI
- Démo Gateway + Evidence Pack
- Plan de mise en conformité AI Act
- Aucune installation requise pour la démo
- Vos données restent chez vous
- Pas d’engagement, pas de carte bancaire
- Réponse sous 24 h ouvrées
The questions your CISO will ask.
Everything a security decision-maker wants to know before rolling this out.
Hosted in the European Union (database and compute in an EU region, encrypted backups in France). No transfer of your business data outside the EU. The few non-EU processors (Copilot/Resend/Sentry) operate under standard contractual clauses and never receive sensitive data — the detail is in our DPA.
It recognises only the domain of the AI tools visited (e.g. chat.openai.com) and the timestamp, in order to map Shadow AI. It never reads your passwords, banking details, the content of your prompts or your non-AI browsing. Minimisation by design: it recognises tools, not people.
AI system register, risk classification (Annex III), DPIA, immutable audit log and signed, timestamped Evidence Packs. The monitoring engine continuously folds in legal developments (AI Act, EUR-Lex) so your compliance stays current rather than frozen at rollout.
The extension scans a device in 60 seconds, with no configuration. Onboarding support (Business/Enterprise) sets up the register and your first policy in a single session.
Encryption in transit (TLS 1.2+), password hashing (Argon2id), strict per-organisation isolation (fail-closed row-level security), MFA available, immutable audit logs, encrypted backups. Tenant isolation is verified by automated tests on every release, run with a role genuinely subject to the database policies.
Discovery is a 14-day Shadow AI audit, free and without a card (Shadow AI scanning, 5 systems, unlimited reporting). After 14 days the workspace becomes read-only — nothing is deleted, your data stays readable and exportable, and you activate a plan when you decide to. Starter €490/month excl. VAT — 20-system register, 10 vendors assessed. Business €990/month excl. VAT — unlimited systems and vendors, unlimited Evidence Packs, Validity. Enterprise from €2,400/month excl. VAT — multi-entity, SSO, contractual SLA. Hosting entirely in the EU · 2 months free on annual billing · 12-month or flexible commitment (+20%). Founders programme: the first 10 organisations lock their price for 24 months — more value, never a discount.
Start by seeing. The rest follows.
Explore the demo in one click, then install the extension and see what is actually happening across your organisation.
SiyadAI Intelligence · Brief de gouvernance IA
Recevez le briefing gouvernance IA
Every fortnight, the AI signals CISOs and executives need: Shadow AI, risks, AI Act developments.